DBeaver: Public Key Retrieval Is Not Allowed (MySQL 8 / 8.4 Fix)
Fix DBeaver's 'Public Key Retrieval is not allowed' error: set allowPublicKeyRetrieval=true, or use TLS. MySQL 8.0, 8.4 and 5.7 differences explained.

- Louis
- 5 min read
- Affiliate Disclosure

Short answer: In DBeaver, open Edit Connection → Driver properties, set allowPublicKeyRetrieval to true, and reconnect. This is not a wrong-password error. MySQL 8+ uses caching_sha2_password, and MySQL Connector/J refuses to fetch the server’s RSA public key unless you allow it or use a secure connection. If you can turn on TLS instead, do that — it is the better fix.
Copy-paste JDBC URL form:
jdbc:mysql://HOST:3306/DB?allowPublicKeyRetrieval=true&sslMode=REQUIRED
The fix, step by step
- Right click on the database connection that you want to connect to.
- Select Edit Connection from the menu.
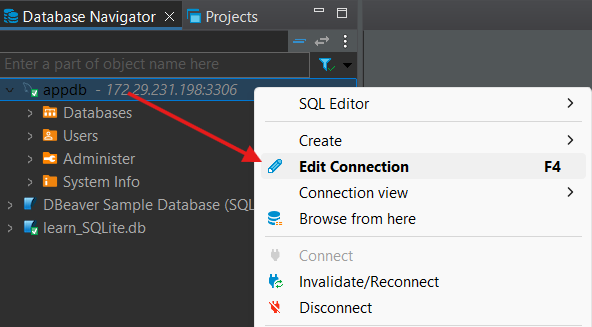
- Switch to the Driver properties tab.
- Set the allowPublicKeyRetrieval parameter to TRUE.
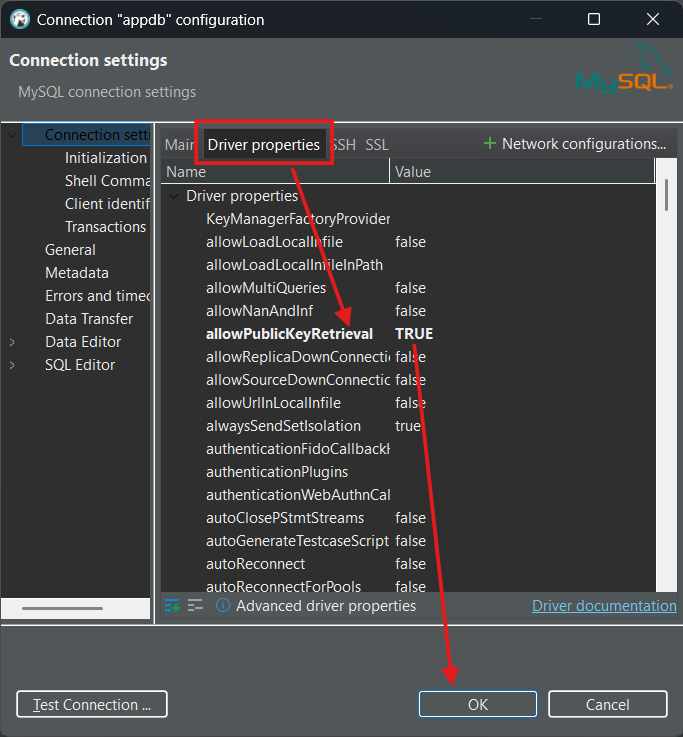
- Click OK, then reconnect.
If the property is not listed, add it as a user property, or use the JDBC URL above (DBeaver: Edit Connection → General → JDBC URL). Test the connection again.
Screenshots are from the version of DBeaver shown in this post. Newer builds may place Driver properties under a different tab, but the property name is the same — it belongs to MySQL Connector/J, not to DBeaver.
MySQL 8.0 vs 8.4 vs 5.7 — what actually changed
The same error has different context depending on the server version:
| Version | Default authentication plugin | What this means here |
|---|---|---|
| MySQL 5.7 | mysql_native_password | This error normally cannot occur. If you see it, the account was switched to a SHA-2 plugin or you are connecting with an 8.x client library |
| MySQL 8.0 | caching_sha2_password (since 8.0.4) | The usual case. Either allow public key retrieval or use TLS. Older tutorials use default_authentication_plugin to switch the server back |
| MySQL 8.4 | caching_sha2_password | Same client-side fix. But mysql_native_password is disabled by default, and default_authentication_plugin is gone |
| MySQL 9.0 | caching_sha2_password | mysql_native_password has been removed |
MySQL’s own rule: to connect with a
caching_sha2_passwordaccount you need “either a secure connection or an unencrypted connection that supports password exchange using an RSA key pair.” — MySQL 8.4 Reference Manual
The MySQL 8.4 trap
A lot of old advice says to run SET GLOBAL default_authentication_plugin = mysql_native_password. On 8.4 that variable no longer exists — the default is controlled by authentication_policy, and the server-side native plugin is disabled unless the server is started with --mysql-native-password=ON. Trying to create or alter an account with that plugin returns ERROR 1524 (HY000): Plugin 'mysql_native_password' is not loaded.
Don’t downgrade the server’s authentication to fix a client setting. Change the connection instead.
Is allowPublicKeyRetrieval=true safe? Three options, best first
allowPublicKeyRetrieval has defaulted to false since Connector/J 5.1.31. Fetching a public key from an untrusted server over plaintext opens a man-in-the-middle path for your password. Note that sslMode defaults to PREFERRED (since 8.0.13), which means Connector/J can silently fall back to an unencrypted connection.
| Option | Setting | When to use |
|---|---|---|
| A. Use real TLS (recommended) | sslMode=REQUIRED, or stricter VERIFY_CA / VERIFY_IDENTITY | Production, any untrusted network. With a secure connection, the RSA key exchange is not needed |
| B. Supply the key locally | serverRSAPublicKeyFile=/path/to/public_key.pem | Managed environments where you can distribute the server’s public key |
| C. Allow retrieval | allowPublicKeyRetrieval=true | Local development and trusted networks only. Pair it with sslMode=REQUIRED as shown above |
The legacy useSSL / requireSSL / verifyServerCertificate flags are deprecated; sslMode replaces them.
What allowPublicKeyRetrieval=true does
- The client knows it may fetch the key. Connector/J checks the property. At its default
false, it will not request the public key, and you get this error. - It requests the server’s RSA public key during connection initialization.
- It encrypts the password with that public key.
- The server decrypts and authenticates with its private key.
What this won’t fix
Access denied for user— that is credentials or grants, not key exchange.- Host unreachable, wrong port, firewall, or a container not exposing 3306 — the connection never reaches authentication.
- A missing or mismatched driver — use a MySQL 8+ driver; a 5.x driver does not understand
caching_sha2_password. Unknown system variable 'default_authentication_plugin'on 8.4 — see the 8.4 trap above. The fix is on the client, not the server.- MariaDB — it uses different authentication plugins; this error is a MySQL Connector/J path.
FAQ
Q: What causes “Public Key Retrieval is not allowed” in DBeaver?
A: A MySQL account using caching_sha2_password (the default since MySQL 8.0) connecting over a connection that is neither TLS-secured nor allowed to fetch the server’s RSA public key. Connector/J blocks the retrieval by default.
Q: Where do I set allowPublicKeyRetrieval in DBeaver?
A: Right-click the connection → Edit Connection → Driver properties → set allowPublicKeyRetrieval to true. You can also append ?allowPublicKeyRetrieval=true&sslMode=REQUIRED to the JDBC URL on the General tab.
Q: Is allowPublicKeyRetrieval=true safe?
A: It is acceptable on a trusted local or internal network, but it can expose your password in a man-in-the-middle scenario over plaintext. For production, prefer sslMode=REQUIRED or stricter, or supply the key with serverRSAPublicKeyFile.
Q: Does MySQL 8.4 need a different fix?
A: The client-side fix is the same. What changes on 8.4 is that mysql_native_password is disabled by default and default_authentication_plugin no longer exists, so old server-side workarounds fail. Fix the connection, not the server.
Q: Will upgrading DBeaver or changing my password fix it?
A: No. This is a Connector/J connection property and an authentication-plugin behaviour. Restarting MySQL, resetting the password, or reinstalling DBeaver leaves the property at false.
Q: Can I fix this without allowing public key retrieval?
A: Yes. Use a TLS connection (sslMode=REQUIRED, VERIFY_CA or VERIFY_IDENTITY), or point serverRSAPublicKeyFile at a locally stored copy of the server’s public key. Both avoid the extra handshake.
Sources & last verified
Last verified: 2026-11-11.
- MySQL Connector/J — Security configuration properties (
allowPublicKeyRetrieval,serverRSAPublicKeyFile,sslMode) - MySQL 8.4 Reference Manual — Caching SHA-2 Pluggable Authentication
- MySQL Reference Manual — Native Pluggable Authentication (deprecated 8.0.34, disabled by default in 8.4, removed in 9.0)
